CYBERSECURITY ACROSS THE CORVINA PLATFORM
Cybersecurity for connected machines
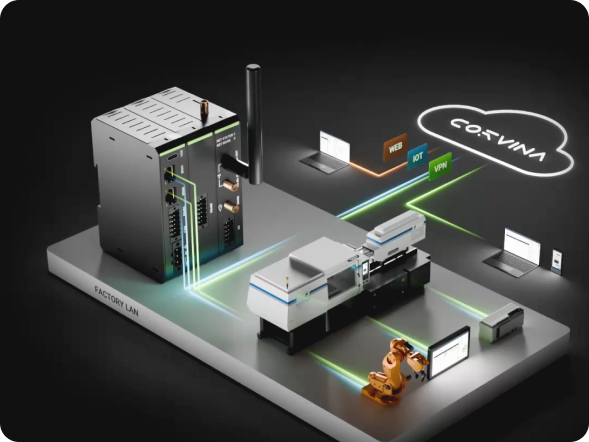
CORVINA brings connectivity, data, users, applications and edge devices together in one industrial IoT platform; with cybersecurity integrated across the way machines are connected, accessed and managed.
CONNECT
CONTROL
MANAGE
MONITOR
CYBERSECURITY ACROSS THE MACHINE LIFECYCLE
Security does not stop at the connection
A connected machine changes continuously throughout its operational life. Users change. Software evolves. Applications are updated. New services are introduced. Machines exchange data with different systems.
CORVINA provides the digital environment to manage these interactions with security, control and traceability throughout the machine lifecycle.
DESIGN
Build connectivity with security in mind
CONNECT
Connect machines securely
OPERATE
Control who can do what
MAINTAIN
Support machines without opening uncontrolled access
UPDATE
Keep software and applications current
MONITOR
Maintain visibility over connected operations
MANAGE
Keep control throughout the machine lifecycle
Why it matters
Cybersecurity is becoming a design requirement.
Industrial machines are no longer isolated assets. They are connected, updated, integrated with IT/OT networks and increasingly managed across their full operational life.
Reduce exposure
Limit unnecessary services, ports, protocols and access points from the earliest architecture decisions.Control access
Manage users, roles, sessions, authentication and permissions across HMI and device environments.Protect integrity
Support software authenticity, project protection, secure update packages and data protection.Manage lifecycle
Address vulnerability handling, updates, documentation and long-term support as part of the product lifecycle.CYBERSECURITY BUILT ACROSS THE PLATFORM
One platform, Multiple layers of protection
Cybersecurity in CORVINA is not a standalone feature or a single product. It is distributed across the platform capabilities used to connect machines, manage users, exchange data, maintain edge devices and deliver digital services.
This allows machine builders to approach cybersecurity as part of their connected-machine architecture rather than as an additional layer added afterwards.
SECURE CONNECTIVITY
Connect machines without losing control
Securely connect industrial devices, machines and remote users while maintaining control over how connections are established and used.
- Secure VPN
- HTTPS and protected web
- communication
- Controlled remote access
- Remote assistance enable/disable
- Industrial connectivity
IDENTITY & ACCESS
Control who can access machines and services
Manage identities, organizations, roles and permissions across distributed machines and customer environments.
- User and role management
- Granular permissions
- Multi-factor authentication
- External authentication services
- Multi-tenant organization
DATA & COMMUNICATION
Protect the path between machine data and digital services
CORVINA provides the connectivity layer through which machine data can securely move from industrial assets to connected applications and services.
- Controlled machine connectivity
- Protected communication channels
- Data access governance
- Machine-to-cloud communication
- Integration with connected services
EDGE & APPLICATION MANAGEMENT
Keep distributed software under control
Manage connected edge devices, applications and software remotely throughout their operational lifecycle.
- Device management
- Application deployment
- OTA updates
- Security patches
- JMobile project updates
WHY IT MATTERS
Connected machines create more relationships to manage
As machines become connected, cybersecurity is no longer limited to protecting a single device. OEMs must manage users, customer organizations, remote connections, applications, software updates, machine data and digital services throughout the installed lifecycle.
Control Access
Define who can access machines, services and data.
Manage Change
Keep applications, software and edge systems controlled as they evolve.
Protect Communication
Manage secure interactions between machines, users and connected services.
Maintain Visibility
Keep connected operations traceable across distributed machine fleets.

SECURITY, GOVERNANCE AND REGULATION
Cybersecurity goes beyond technology
CORVINA combines platform capabilities with structured information-security and cybersecurity processes to support the management of connected industrial assets throughout their lifecycle.
- ISO/IEC 27001
Information security management approach for Corvina Cloud and cloud-connected industrial services. - ISA/IEC 62443 principles
Industrial cybersecurity principles supporting secure automation and connected machine architectures. - CRA readiness
Support for vulnerability management, software updates, documentation, and post-market monitoring processes. - NIS2 awareness
Support for stronger access governance, risk management expectations, and supply chain cybersecurity processes. - Machinery Regulation readiness
Support for controlled remote access and protection of machine-related operations.
Use cases
Where CORVINA supports cybersecurity in daily operations
CORVINA is designed for OEMs and industrial organizations that need to scale secure access, services and lifecycle activities across many customers, sites and machines.
Remote troubleshooting
Fleet update management
Multi-customer environments
OEM after-sales service
Documentation delivery
Post-market lifecycle
CORVINA + EXOR
Start from secure industrial technology
Documents, certificates and resources
A scalable area for
cybersecurity content
Use this section as a future-ready resource center for certificates, policies, technical notes, security guidelines, webinar recordings and customer-facing documents.
FAQ
Everything you should know.
CORVINA enables controlled remote access to industrial devices, helping service teams perform diagnostics and troubleshooting while maintaining user and permission governance.
Yes. CORVINA supports user and role management, allowing organizations to define who can access specific machines, services and data.
Yes. CORVINA can support optional two-factor authentication to strengthen access protection.
Corvina Edge Manager helps manage connected edge devices centrally, including software updates, application deployment, patching and lifecycle operations.
It allows machine documentation and software to be stored, versioned and accessed in a controlled way, supporting documentation consistency and lifecycle management.
Yes. Remote connection can be controlled through software logic or by integrating a hardware switch in the machine application.
No. Remote access is one part of the platform. CORVINA also supports data collection, user governance, edge management, software updates, documentation and connected asset lifecycle management.
No platform alone can guarantee compliance for a complete machine or organization. CORVINA supports cybersecurity-oriented processes such as access governance, traceability, update management and lifecycle control.
Corvina can provide documented evidence across all the main areas of a supplier security assessment. Alongside the ISO/IEC 27001:2022 certification, formal policies are in place for acceptable use, information classification and labelling, transfer and deletion, clear desk, HR security, legal and regulatory requirements and intellectual property, physical security, cryptography, secure development lifecycle, secure coding, data masking, outsourced development and access to source code. Configuration management is covered by policy and by an operating procedure for the infrastructure. A formal risk assessment methodology and a company-level risk assessment are maintained. Detailed documentation is available under authorisation, which can be requested at security@holdex.it
Vulnerability assessments and penetration tests are performed periodically, with formal remediation tracking in a ticketing system. STRIDE-based threat modelling is embedded in the product development lifecycle. Secure coding practices follow OWASP guidance, and cryptography adopts NIST SP 800-131A and SP 800-57.
Platform availability status is published at https://corvina.instatus.com
Incident handling is covered by a group-level notification procedure and an incident response policy, with operational playbooks for the main scenarios, including loss of data availability or integrity, data breach in third-party SaaS, customer data leak, and hardware theft or loss. Our internal CSIRT is formally approved by top management and registered with the Italian national cybersecurity authority (ACN).
Take control of connected
machine cybersecurity
EXOR + CORVINA
Extend cybersecurity from the device to the connected asset